

PHPの脆弱性が大きな注目を浴びた一週間でした。
私もWordPressのサイトを複数運営しているので、対応が必要となりました。
【English】
This week, news spread about two serious vulnerabilities in PHP, the language that powers a huge share of the web, including WordPress. I run a few WordPress sites myself, so I couldn’t just read the headlines and move on. I needed to check whether my own sites were safe.
I’ll admit I felt uneasy at first. The flaws were described as critical, and some web services in Japan even went into emergency maintenance. For a moment, I imagined spending a considerable time on the daunting task of fixing things.
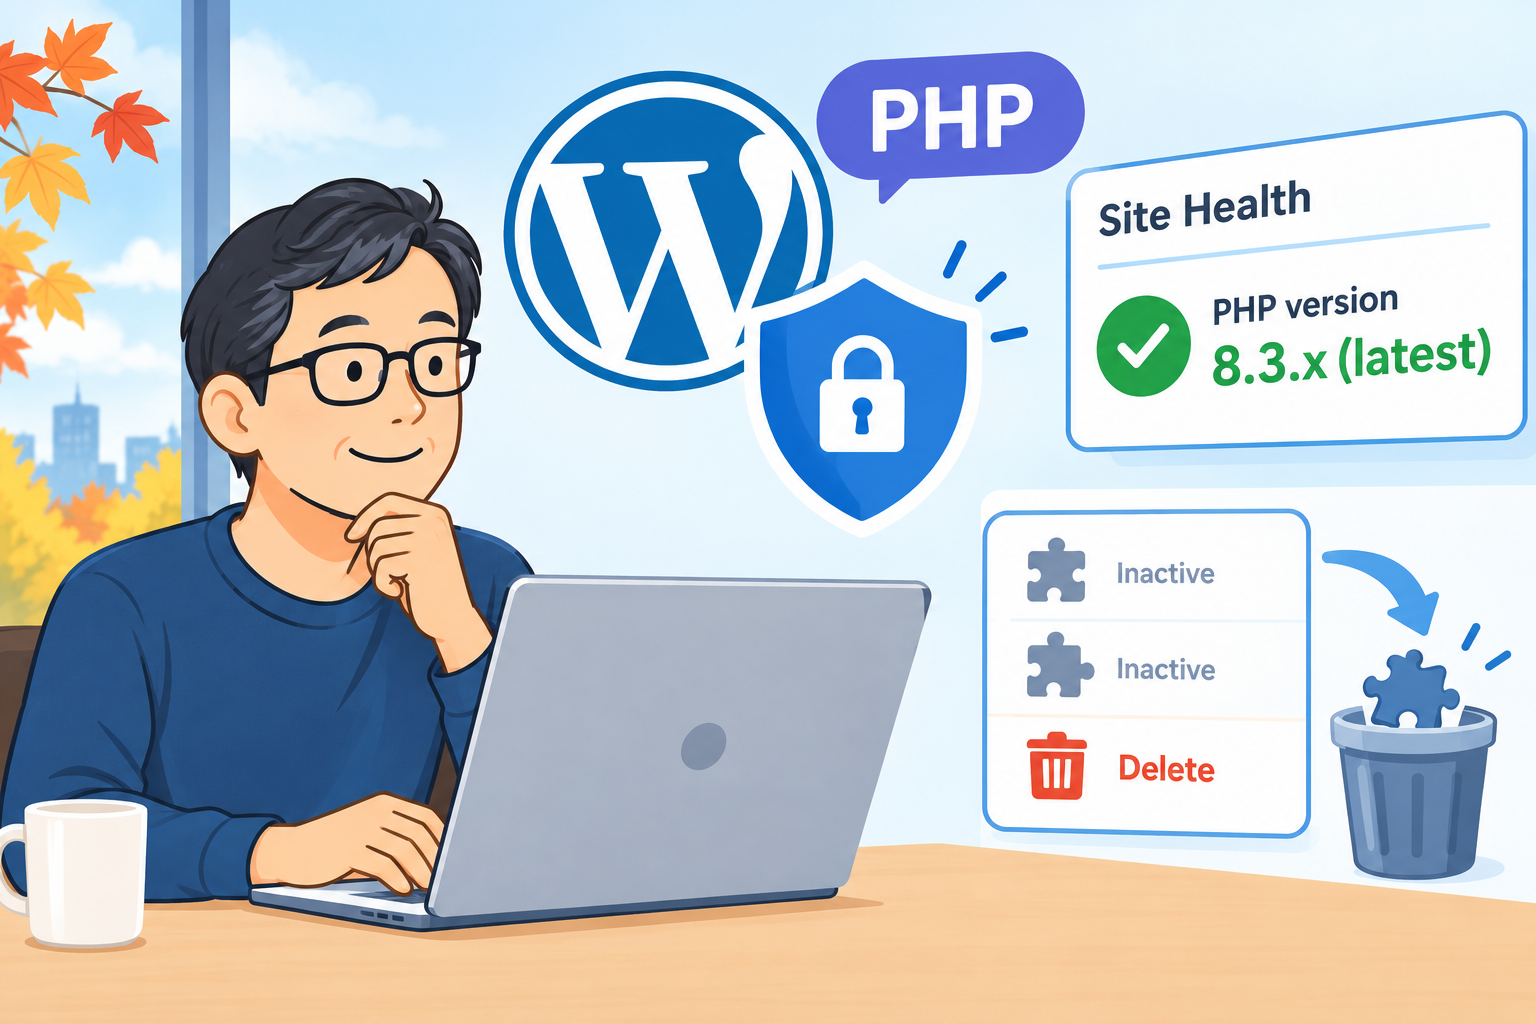
Fortunately, it turned out to be much simpler than I feared. My sites were running a version of PHP that was still supported, so my hosting company had already applied the security patch on their side. I logged in to the WordPress dashboard, opened Site Health, and confirmed that PHP was on the latest patched release. It was a quiet relief to see that number on the screen.
I briefly considered an upgrade to the latest major version of PHP. In the end, I decided to stay where I was. Even though it’s not the latest version, official support is still available and has been maintained for a couple of years. In addition, I wasn’t sure all my plugins would get along with it. Stability felt more important than novelty.
Still, the whole episode made me look at my sites a little more carefully. I realized I had several plugins I wasn’t using anymore. Until now, I had simply deactivated them, thinking that was enough. But deactivated plugins still sit on the server, quietly waiting to become a risk. So this time, I deleted them.
Sometimes a scare is just the reminder we need. It keeps us grounded and more careful going forward.
コメント